



SaaS Application Development: Process, Cost, And Architecture

KEY TAKEAWAYS:
- SaaS application development turns a repeatable customer outcome into a managed cloud service with subscriptions, tenant access, security, integrations, and ongoing operations.
- The first release should prove one valuable workflow with a clear user, outcome, acceptance criteria, and learning target.
- SaaS can improve distribution and updates, but the provider also absorbs uptime, support, security, billing, and cost-to-serve responsibility.
- Multi-tenancy is a set of isolation decisions across identity, application code, data, files, jobs, logs, analytics, and support access.
- Cost and timeline depend on scope, integrations, data readiness, security, tenancy, team capability, and operational risk, not screen count alone.
Customers rarely pay for SaaS simply because it runs in the cloud. They pay for a repeatable outcome delivered with less operational effort than building and maintaining the capability themselves. That makes SaaS application development a product, commercial, and operations problem at the same time: the workflow must be valuable, access must be predictable, data must be isolated, and the provider must be able to support the service after launch.
What Is SaaS Application Development?
SaaS application development is the process of designing, building, deploying, and operating cloud software that serves customers through a recurring subscription, usage-based charge, or hybrid commercial model. The provider owns the application and service operations, while customers access the product through a browser, mobile app, API, or connected workflow.
The work includes much more than frontend and backend code. A production SaaS product must handle organization accounts, tenant boundaries, identity, roles, plans, billing events, entitlements, integrations, backups, monitoring, support, and safe releases. The product is successful only when customers can repeatedly complete the job they paid for and the provider can operate that service at a sustainable cost.
A useful distinction is between a hosted application and a SaaS business. Hosting software online does not automatically make it SaaS. SaaS adds a managed service relationship: customers receive ongoing access, updates, support, and operational continuity without running the whole system themselves. A dedicated customer deployment can still be SaaS when the provider manages it as part of a repeatable product and service model.
Before a large build, clarify the product hypothesis with a POC vs MVP vs Prototype: How To Choose The Right Step decision. The goal is not to create a smaller feature list. It is to identify the smallest complete service that can test a valuable customer outcome.
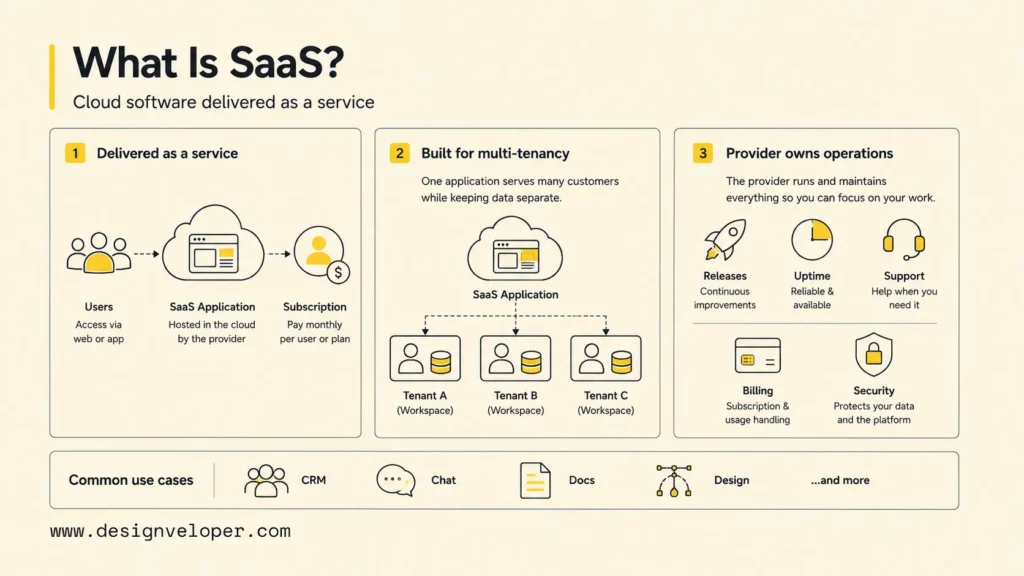
The overview is best read as a connected system: product scope drives architecture, architecture affects cost, and operations determine whether the service remains reliable after the first release.
For a deeper dive:
- How To Build An App For Your Business: 10-Step Guide
- Web App vs Website: Similarities, Differences and Misconceptions
- What Is GraphQL? A Detailed Guide
What Are SaaS Applications?
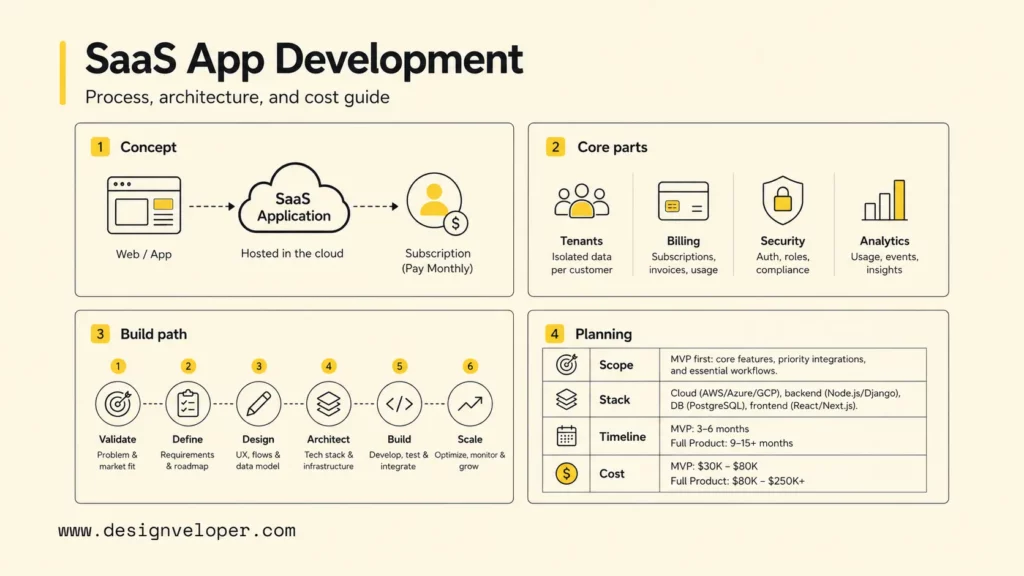
SaaS applications are cloud-based software products that many customer accounts can access through a managed service. Google Workspace, Microsoft 365, Slack, Salesforce, Shopify, Figma, and focused business platforms are familiar examples. The industry does not define SaaS; the ongoing relationship between provider, tenant, software, data, and subscription does.
A tenant is usually an organization, workspace, customer account, or business unit. It can contain users, teams, roles, documents, workflows, integrations, subscription states, and support history. A SaaS platform may use pooled resources, dedicated resources, or a hybrid model. The important requirement is that every request, job, file, cache entry, event, and support action respects the intended tenant boundary.
- Shared service: the provider manages infrastructure, application releases, availability, and security updates.
- Tenant-aware access: customers can work in their own organization context with the roles and policies that apply to them.
- Recurring value: the service supports a workflow customers expect to use repeatedly, not just a one-time transaction.
- Commercial state: plans, invoices, trials, usage, entitlements, renewals, and cancellations influence product access.
- Continuous operation: monitoring, support, incident response, migration, and maintenance continue after launch.
This operating model changes product responsibility. A packaged application can wait for a later release to address a defect. A SaaS provider must handle the defect while customers are already using the service, often across different plans, regions, integrations, and data volumes.
The tenant relationship shown here should be reflected in the data model, authorization checks, billing model, analytics, and support tools rather than treated as a marketing description only.
SaaS Benefits, Trade-Offs, And Use Cases
SaaS is attractive because it can turn software distribution into an ongoing relationship, but the model also moves more responsibility to the provider. Evaluate both sides before choosing the architecture or pricing approach.
Why Businesses Choose SaaS
- Lower adoption friction: customers can start through a managed account instead of installing and operating the full system.
- Continuous improvement: the provider can release fixes, integrations, security updates, and product improvements through one service.
- Predictable access model: plans, roles, usage limits, and support can be packaged around the customer’s workflow.
- Shared product learning: usage signals and feedback can guide improvements across a customer segment without copying one-off deployments.
What The SaaS Provider Must Absorb
The provider becomes responsible for availability, data protection, support, incident response, migrations, billing accuracy, vendor dependencies, and a reliable release process. A customer may judge the product by one failed export, an unclear payment state, a slow integration, or an unresolved permission issue even when the main feature works.
Shared infrastructure can improve utilization, but it creates noisy-neighbor, isolation, quota, and support-access risks. Dedicated resources can satisfy stronger performance or customer requirements, but they raise deployment and operating cost. The correct choice depends on evidence, not on a blanket preference for shared or dedicated environments.
Where SaaS Fits Best
SaaS is a strong fit when many customers share a repeatable job with configurable rules, such as project collaboration, scheduling, finance operations, customer support, logistics coordination, analytics, or document workflows. It is less suitable when every customer needs a fundamentally different product, must control the whole deployment, or cannot accept the provider’s data and operating model.
For a regulated or highly customized market, a managed dedicated deployment may be a better commercial form than a fully pooled service. It can still follow SaaS principles if the provider standardizes deployment, updates, support, billing, and lifecycle ownership.
Core SaaS Application Features
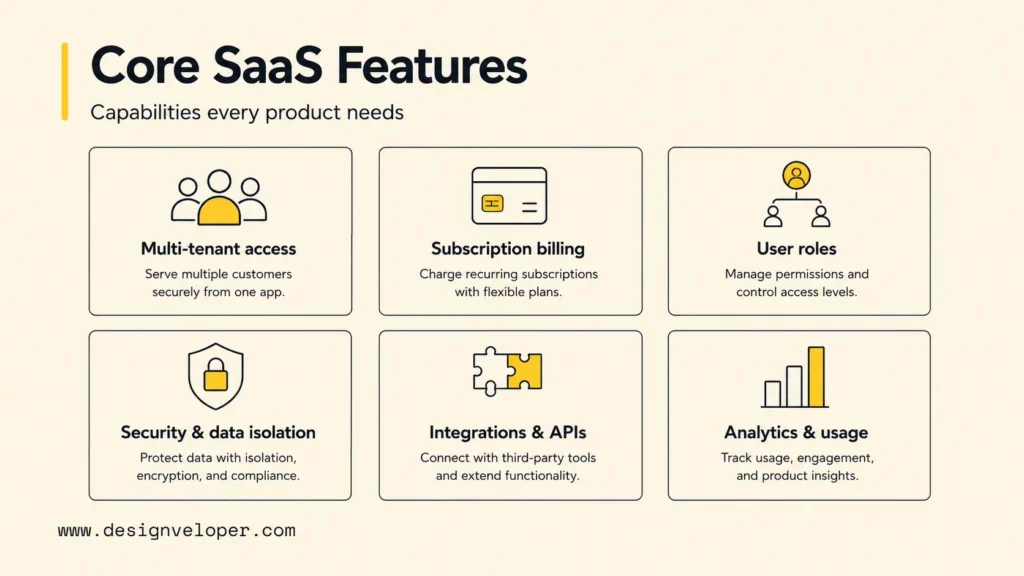
A useful SaaS feature set connects the customer workflow to the provider’s ability to operate it. The exact features depend on the product, but the following capabilities appear in most serious SaaS planning conversations.
- Tenant-aware access: carry tenant identity through requests, queries, caches, files, queues, logs, and background jobs. AWS describes tenant isolation as a foundational SaaS concern because shared infrastructure must not expose one customer’s resources to another.
- Identity and roles: support signup, invitations, organization membership, ownership, role changes, session management, MFA, SSO, support access, and audit history where the product requires them.
- Subscriptions and entitlements: connect plans, trials, invoices, usage limits, upgrades, downgrades, payment failures, grace periods, and cancellations to explicit product permissions.
- Security and data protection: protect secrets, encrypt data where appropriate, validate authorization, log sensitive actions, control retention, and rehearse backup restoration and incident response.
- Integrations and APIs: define contracts, webhooks, idempotency, retries, rate limits, versioning, error handling, and ownership for every external dependency.
- Product analytics: measure activation, completion of the core workflow, adoption depth, account health, support friction, retention signals, and cost-to-serve with safe tenant dimensions.
- Release and operations: provide environments, migrations, feature flags, health checks, monitoring, alerts, support tools, rollback plans, and customer communication.
Automatic updates are valuable only when change is controlled. Customers may depend on permissions, exports, integrations, and workflow behavior that a release could break. Backward compatibility, migration planning, staged rollout, release notes, and support readiness belong in the feature definition.
For security planning, pair the product checklist with What Is Web Application Security? OWASP 10 Web App Vulnerabilities and map only the controls that match the product’s risk and data scope.
The feature groups overlap by design. For example, a plan change affects entitlements, UX, billing events, audit records, analytics, support, and possibly resource allocation.
Key Decisions Before SaaS Application Development
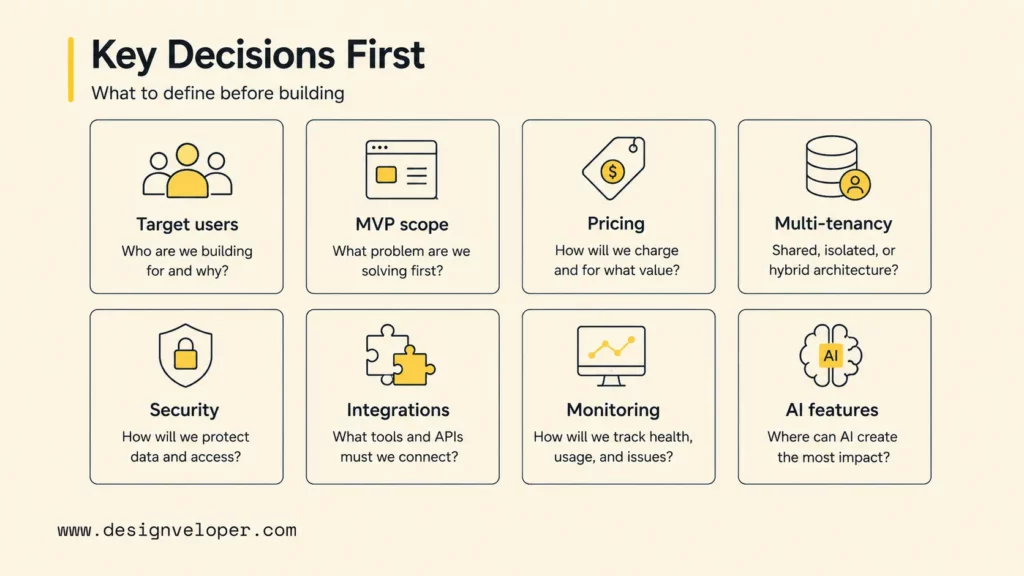
The most expensive SaaS mistakes often begin as unexamined assumptions. Capture product, commercial, architecture, and operational decisions together before the team commits to a large build.
| Decision area | What to define | Evidence to collect |
|---|---|---|
| Customer and problem | Buyer, daily user, painful job, current alternative, and desired outcome | Observed workflow, recent examples, pilot interest, and disconfirming evidence |
| MVP boundary | One complete workflow, roles, acceptance criteria, excluded features, and pilot group | Task completion, repeat use, payment intent, and support load |
| Pricing and access | Value metric, plans, trials, entitlements, usage limits, and failed-payment behavior | Buyer expectations, margin model, billing accuracy, and reconciliation rules |
| Tenancy and data | Pooled, siloed, or hybrid isolation for compute, data, files, jobs, and analytics | Security, compliance, performance, customization, migration, and unit-cost needs |
| Integration and operations | Systems of record, owners, contracts, recovery, service objectives, and telemetry | Sandbox access, dependency risks, failure drills, and support responsibilities |
Multi-tenancy is not one binary choice. Azure’s tenancy model guidance explains that a solution can share some layers while isolating others. A pooled application tier can use a dedicated database for a sensitive customer; a shared database can still enforce tenant-aware access with different resource controls. Select isolation per layer when the requirements justify it.
Pricing also belongs in the domain model. A per-seat product needs seat assignment and entitlement events. A usage-based product needs accurate metering, late-event handling, aggregation, customer-visible usage, overage rules, and billing reconciliation. Stripe’s billing documentation covers subscriptions, usage, invoices, and customer portals, but the SaaS product remains responsible for translating billing state into safe access.
A SaaS MVP is the smallest complete service that can prove a valuable, repeatable customer outcome.
The planning decisions below turn that principle into a delivery boundary: what the team will prove now, which risks need evidence, and which capabilities can wait.
This planning model keeps architecture discussions connected to evidence. If a decision has no user, risk, cost, or operational reason behind it, it may be premature for the first release.
A Practical SaaS Project Example
Consider a B2B approval workflow for a company that currently manages requests through email and spreadsheets. The example is intentionally concrete because SaaS architecture becomes easier to evaluate when the team can trace one request from signup to measurable business value.
Example: B2B Approval Workflow
- Actor and input: an employee submits a request with a category, amount, documents, and business reason.
- System action: the service validates the tenant, checks the requester’s role, routes the request to the right approver, and records each state change.
- Decision: an approver accepts, rejects, or returns the request for more information; high-value requests require an additional approval.
- Outcome: the requester sees a clear status, the finance system receives an approved event, and administrators can audit the complete history.
- Limitation: the first release may support one request type and one finance integration rather than every department and policy variation.
MVP Boundary For The Example
The MVP can include organization signup, invitations, role assignment, one request form, one approval path, status notifications, an audit trail, basic subscription access, and one integration. It should also include tenant-aware queries, failed-integration handling, support access, data export, monitoring, and a tested recovery path. A polished dashboard without those controls would demonstrate a screen, not a complete service.
What To Measure After The Pilot
- Time from request submission to a valid decision.
- Percentage of requests completed without support intervention.
- Approval and rejection errors caused by missing permissions or routing rules.
- Integration delivery rate, retry volume, and reconciliation exceptions.
- Repeated use by the target team and willingness to continue under the proposed plan.
This pattern applies to other vertical SaaS products: define the actor, input, controlled workflow, measurable outcome, and limitation before choosing additional features or services.
SaaS Application Development Process
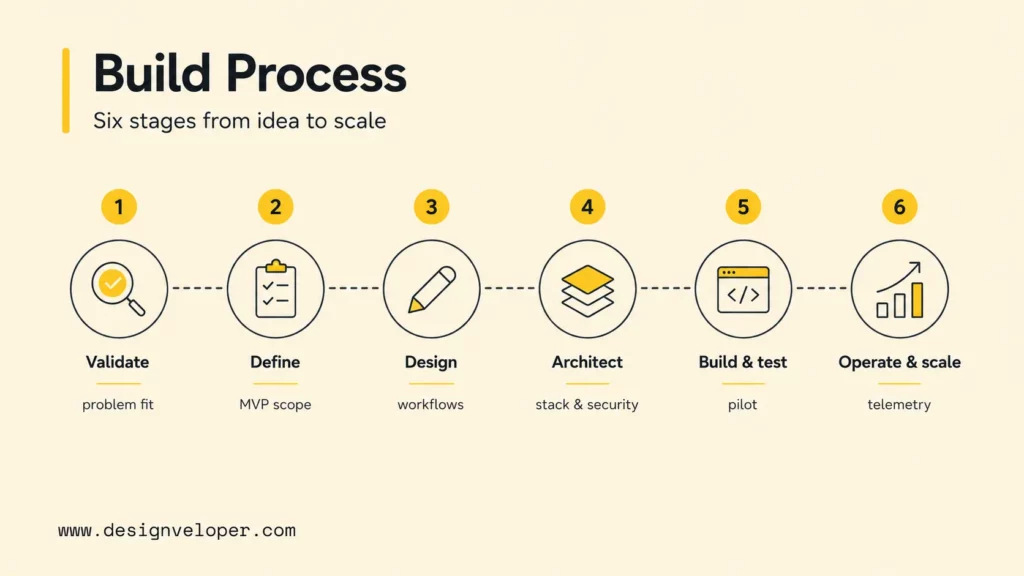
A practical SaaS development process moves through six stages, but the stages are not isolated handoffs. Validation can change scope, a prototype can reveal identity complexity, testing can change architecture, and production telemetry can reorder the roadmap.
Step 1. Validate The SaaS Idea And Target Market
Start with a narrow customer segment and a reachable workflow. Interview buyers, daily users, administrators, and people affected downstream. Observe spreadsheets, email, manual reviews, existing software, delays, workarounds, and failure costs. Recent examples are more useful than opinions about a hypothetical product.
Map the current process and define the outcome in measurable terms: time saved, errors reduced, revenue captured, risk controlled, or a capability made possible. Test demand with a prototype, concierge service, landing page, paid discovery, or pilot. The evidence becomes stronger when customers provide data, staff time, a signed pilot, or payment.
Step 2. Define Requirements, MVP Scope, And Monetization
Turn the validated workflow into roles, states, data, integrations, business rules, and acceptance criteria. Define failure paths such as duplicate events, expired trials, payment failure, permission denial, unavailable integrations, canceled jobs, and partial imports.
Use a vertical MVP slice. For a B2B workflow product, that might mean organization signup, invitations, role assignment, one core workflow, one integration, a plan and checkout, usage events, support access, monitoring, and export. Put speculative customization, secondary integrations, and deep analytics into later hypotheses unless the first customer outcome depends on them.
Step 3. Design UX/UI And SaaS Product Workflows
Design the complete service, not only the primary screen. Map signup, workspace creation, onboarding, empty states, invitations, roles, plan selection, payment, core work, notifications, integrations, support, export, and cancellation. Owners, administrators, managers, contributors, viewers, and support staff may need different permissions and views.
Prototype the highest-risk journeys with realistic data. Test whether users understand the value, finish the job, recover from an error, and know what will happen to their data and subscription. Include responsive behavior, keyboard interaction, accessibility, loading states, retries, and notification choices.
Step 4. Choose The Tech Stack And Cloud Architecture
Choose technologies the team can operate and hire for. A common web stack may use React, Next.js, Vue, or Angular; Node.js, .NET, Java, Go, Python, or Ruby; a managed relational database; object storage; a queue; a cache; and a managed cloud runtime. The product’s constraints matter more than a trend.
Start with a modular monolith when one deployment and database can meet the scale, reliability, and ownership boundaries. Split services only when independent scaling, failure containment, security, technology, or team ownership creates enough value to justify distributed data, networking, tracing, and deployment complexity.
Create threat, data, and tenant-boundary models. Decide where tenant context enters, how it is validated, and how it follows every request, job, query, cache key, file path, webhook, and log. Include backups, recovery, migrations, deployment, telemetry, and cloud cost in the architecture record.
Step 5. Build, Integrate, And Test The SaaS Application
Build vertical slices that cross interface, API, data, permissions, telemetry, and tests. Deliver the riskiest capabilities early: tenant scoping, billing state, external integration, migration, or an AI evaluation loop. Use unit, integration, contract, end-to-end, accessibility, load, and recovery tests where they match the risk.
Security belongs inside delivery. NIST’s Secure Software Development Framework provides a structure for preparing the organization, protecting software, producing secure software, and responding to vulnerabilities. OWASP’s Application Security Verification Standard can turn relevant security expectations into testable acceptance checks.
Test isolation with adversarial cases: substitute tenant identifiers, reuse object IDs, manipulate exports, replay webhooks, inspect search results, and run background jobs under the wrong context. Also test migration rollback, backup restoration, billing reconciliation, rate limits, degraded integrations, and support access.
Step 6. Deploy, Monitor, Maintain, And Scale
Deploy through an automated pipeline with separate environments, tested migrations, secret controls, approvals, health checks, and rollback. GitHub’s deployment environment controls illustrate how approvals, protected secrets, and deployment restrictions can be made explicit.
Instrument critical journeys before launch. OpenTelemetry defines traces, metrics, and logs as core telemetry signals; apply tenant-aware dimensions carefully so personal data and secrets do not leak into operational data. Monitor availability, latency, errors, queue delay, integration failures, billing events, backup status, cloud spend, and product value events.
Launch gradually with internal accounts, design partners, feature flags, or a percentage rollout. Prepare incident ownership, support tools, status communication, and recovery exercises. Scale based on measured bottlenecks: optimize queries, move slow work to queues, apply rate limits, partition workloads, or add dedicated resources when the evidence supports the change.
A stage is complete when it produces evidence for the next investment: validated demand, a bounded MVP, tested workflows, an architecture decision, verified vertical slices, or reliable production signals.
Related reading:
- Software Development Costs: Guide to Estimate Your Project
- How To Develop A Low-Code MVP: Practical Step-By-Step Guide
- AI In Product Development: From Concept To Market Faster
SaaS Architecture And Tech Stack
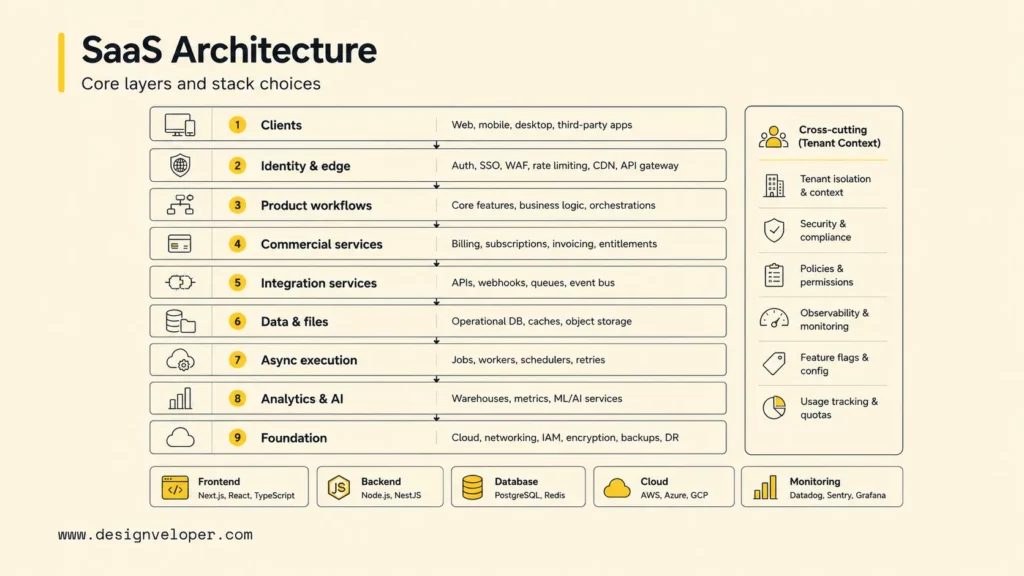
A SaaS architecture should carry tenant identity, policy, commercial state, and telemetry through every layer. A small product can keep several layers in one deployable application while preserving clear boundaries in code, data, and operations.
| Layer | Common choices | What to decide |
|---|---|---|
| Frontend | React, Next.js, Vue, Angular, native or cross-platform mobile | Rendering, accessibility, offline behavior, design system, state, and release model |
| Backend and APIs | Node.js, .NET, Java, Go, Python, REST, or GraphQL | Domain boundaries, contracts, jobs, idempotency, authorization, and versioning |
| Data and files | PostgreSQL, MySQL, document stores, object storage, cache, and search | Tenant key, transactions, residency, encryption, retention, backup, and restore |
| Tenancy model | Pooled, database-per-tenant, stack-per-tenant, or hybrid | Isolation, customization, noisy neighbors, quotas, migration, and unit cost |
| Identity and policy | OIDC/OAuth, SAML SSO, MFA, RBAC, or policy engine | Membership, least privilege, support access, audit, and account recovery |
| Commercial services | Subscription provider, usage meter, invoices, and entitlement module | Catalog, price, tax, plans, retries, grace periods, and reconciliation ownership |
| Cloud and operations | Managed runtime, containers, queues, CI/CD, monitoring, and infrastructure as code | Regions, environments, recovery, deployment, alerts, and cost controls |
Pooled resources improve utilization and simplify fleet operations, but require rigorous tenant-aware authorization and resource controls. Siloed resources improve physical separation and can help with custom compliance or performance needs, but increase deployment count and cost. A hybrid model shares most layers while dedicating selected databases, storage, compute, or model resources to particular customer tiers.
Choose the simplest architecture that can meet the first service objective, then keep a path between models. A successful pooled product may later offer dedicated databases to enterprise tenants. That transition is easier when tenant ownership is explicit, migrations are automated, and services do not assume one global database.
Use a modular monolith when it keeps transactions, local development, and ownership clear. Move to separate services when independent scaling, failure containment, data access, or team boundaries create measurable value. More services do not automatically mean more scalability; they create more contracts and operational work.
The architecture image is a logical map rather than a mandatory service diagram. Preserve the responsibilities even when the first implementation uses fewer deployable components.
SaaS Application Development Cost And Timeline
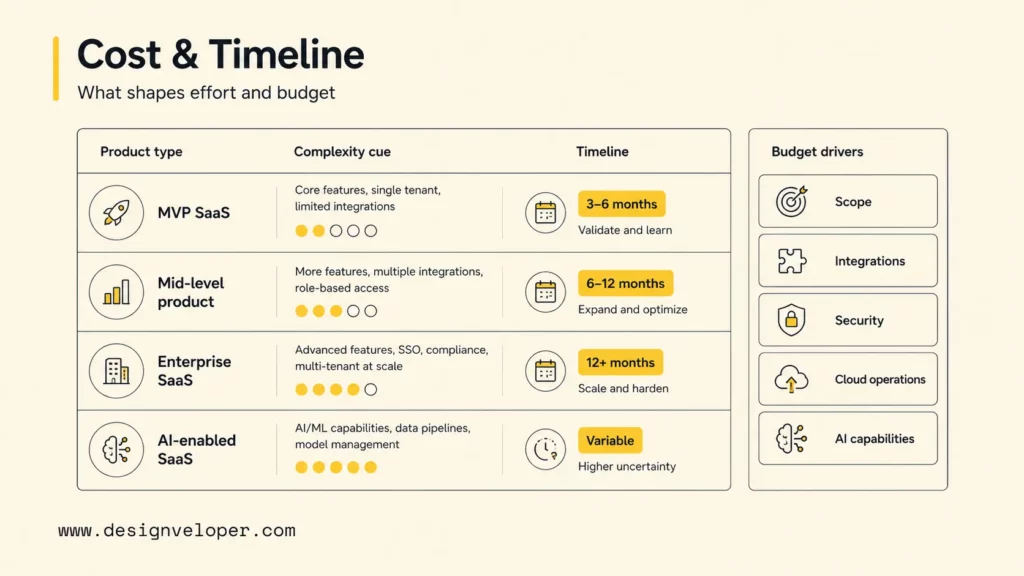
There is no useful SaaS development price or delivery date without a defined workflow, team capacity, integration access, and operating assumptions. Estimate the build and the recurring service separately. The approval-workflow example above provides a concrete scope to price without borrowing an unrelated market average.
| Product scope | Typical complexity | Main cost and timeline drivers |
|---|---|---|
| Focused MVP | One segment, one core workflow, basic roles, subscription, and limited integrations | Validation, UX, core engineering, security baseline, billing, testing, and launch support |
| Mid-level SaaS | Several workflows, richer roles, dashboards, public API, and multiple integrations | Data migration, automation, support tooling, integration recovery, and performance |
| Enterprise SaaS | SSO, advanced policy, audit, dedicated resources, migration, compliance, and service commitments | Procurement, deployment options, data residency, security evidence, and operations |
| AI-enabled SaaS | Model integration, retrieval or tools, evaluation, safety, human review, and variable inference cost | Data readiness, acceptable failure, evaluation, guardrails, model changes, and unit economics |
Build an estimate for the illustrative B2B approval product. Set an assumption sheet first: one customer segment, one request-to-approval path, defined requester/approver/admin roles, a tenant-aware workspace, subscription billing, one finance integration, a pilot tenant count, and a base and peak monthly request volume. Record what is excluded, such as SSO, historical migration, additional regions, and bespoke customer workflows.
- Delivery work packages: discovery and validation; UX and accessibility; tenant-aware identity and authorization; request, review, and audit flow; billing and entitlements; finance integration; security, recovery, and acceptance testing; deployment and pilot support. For each package, record role-specific estimated effort multiplied by the agreed rate, its dependencies, and a confidence level.
- External and risk costs: add vendor setup or certification fees and a visible contingency for uncertain integration, data, and approval work. Do not hide those risks inside a single unexplained total.
- Monthly operating model: calculate base and peak cases for cloud compute, database, storage, email, payment processing, monitoring, integration calls, support, and maintenance using expected tenants and transactions. Add compliance or AI usage only when actually in scope.
- Decision metric: divide the monthly operating total by active paying tenants, or by completed approvals in the same month, and state which denominator you used. Recalculate after the pilot with observed usage and support time.
Delivery estimate = sum of package effort by role times each role’s rate, plus external fees and explicit contingency. Monthly cost to serve = infrastructure and vendor usage plus support, monitoring, maintenance, and expected incident work. This is a worksheet, not a quote: the team must populate effort, rates, usage, and vendor terms before it can yield a currency amount.
Dependencies can dominate the estimate. One external integration may require sandbox access, certification, mapping, webhook recovery, rate-limit handling, and ongoing version maintenance. Enterprise identity, data residency, audit exports, role matrices, and migration can take more effort than several visible screens.
To control cost, fund the riskiest assumptions first, use managed services selectively, keep the first architecture reversible, automate tests and environments, and delay speculative features. Do not cut tenant isolation, backup restoration, monitoring, or secure deployment to make an estimate look smaller; those omissions transfer cost to production.
For the schedule, sequence discovery, the first end-to-end approval slice, tenant-boundary tests, billing and finance integration, recovery testing, and a limited pilot. Estimate each package against actual team availability and external approval windows; identify the critical path rather than adding generic month bands. Revisit effort and dates after the riskiest integration and cross-tenant access tests. Enterprise procurement, SSO, data residency, and audit evidence may extend that path.
Use the visual comparison as a planning conversation, not as a fixed industry benchmark. The same product category can have very different effort when data, security, integrations, or customer commitments change.
Related planning resources:
- 10 Best AI Apps For Work, Research, And More
- How Long Does It Take To Build A Web App? Full Timeline Guide
- AI-Driven Decision Making: Turn Business Data Into Better Action
Aligning SaaS Architecture With Subscriptions, Data, And Growth
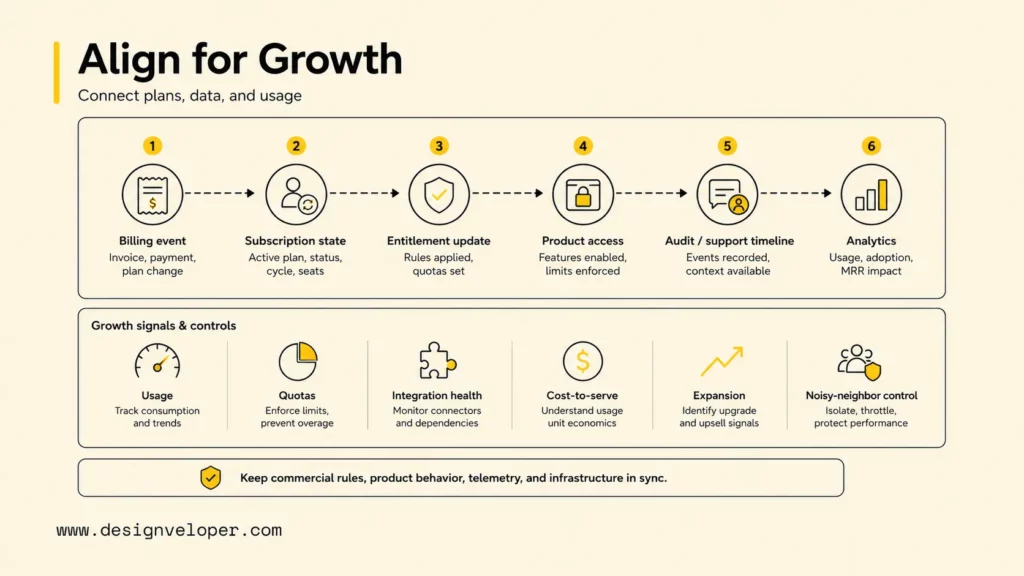
A scalable SaaS product aligns commercial rules, tenant boundaries, product behavior, telemetry, and infrastructure. When those systems evolve independently, customers see inconsistent access, invoices become difficult to reconcile, support cannot explain account state, and cloud cost grows without a clear link to revenue.
Connect Billing Events To Entitlements
Use one product catalog and an explicit entitlement module or service. A plan change should create a traceable sequence: receive and verify the billing event, handle it idempotently, update subscription state, recalculate entitlements, write an audit record, notify the customer, and emit analytics. Support staff need a safe account timeline, not direct database edits.
For example, when a payment fails, store the verified provider event ID and move the subscription into its documented billing state. Apply the published grace-period rule before changing product access; a failed charge alone should not erase a customer’s work. If the webhook is delivered twice, use the event ID to prevent a second state change. If a later paid event arrives out of order or billing and access disagree, retain the event history, alert the billing-reconciliation owner, and resolve the account before support overrides permissions.
Measure Value And Cost Per Tenant
Track value events, active teams, adoption depth, integration health, support friction, expansion, contraction, and cost-to-serve with tenant and plan context. Create budgets and quotas for storage, requests, jobs, exports, AI tokens, and third-party calls. A noisy-neighbor control protects reliability; a cost signal protects margin.
Operate Security, Support, And Change
Assign owners for incidents, access requests, billing reconciliation, backups, integrations, and release decisions. Review recovery and support workflows with the same seriousness as customer-facing features. Data retention, export, deletion, support impersonation, and audit access should have policy, logging, and approval rules.
Designveloper’s software development services can help teams connect MVP scope, user workflows, multi-tenant architecture, subscriptions, integrations, delivery automation, and post-launch operations. A risk-led discovery identifies what to build now, what to postpone, and which assumptions need evidence before more budget is committed.
The commercial flow is part of the product architecture. Keeping it explicit makes changes easier to test, explain, support, and scale.
FAQs About SaaS Application Development
How Long Does It Take To Build A SaaS Application?
It depends on the work packages, available team capacity, and the critical path through data access, integration approval, tenant-boundary testing, security review, and pilot feedback. Estimate and sequence those tasks for the actual scope, then revisit the delivery date after the riskiest integration and isolation tests. A generic month range cannot replace that project schedule.
How Much Does SaaS Application Development Cost?
Calculate build cost from role-specific effort for each delivery package, agreed rates, external fees, and an explicit risk contingency. Then estimate monthly cloud, database, storage, email, payment, monitoring, integration, and support costs at base and peak usage. The approval-workflow worksheet above shows the inputs; without actual scope, rates, and volume, a fixed figure would be misleading.
What Is The Best Tech Stack For SaaS Development?
The best stack meets product constraints and can be operated by the available team. React or Vue with Node.js, .NET, Java, Go, or Python and a managed relational database is common, but not mandatory. Prefer mature ecosystems, managed infrastructure, security support, observability, automated deployment, and a simple architecture until scale or ownership boundaries justify complexity.
How Do You Make A SaaS Application Secure?
Start with threat modeling, tenant-aware authorization, least privilege, secure identity, secret management, encryption, dependency updates, audit logging, backups, recovery tests, and secure development practices. Test cross-tenant access, object references, exports, webhooks, background jobs, support access, and failed authentication. Use a security standard such as OWASP ASVS to turn the relevant controls into acceptance criteria.
Should You Build A SaaS MVP Before A Full Product?
Usually, build the smallest complete service that can test the customer outcome before funding a broad product. The MVP still needs the security, access, billing, support, monitoring, and recovery capabilities required for its real pilot. An MVP is not permission to ignore production responsibilities; it is a way to limit unproven scope.
The Practical Answer
SaaS application development succeeds when product value, tenant boundaries, subscriptions, architecture, security, and operations are designed as one service. Start with one measurable workflow, validate the commercial assumption, choose the simplest architecture that can support the pilot, and make billing, access, monitoring, and recovery explicit before launch. Then use customer behavior and operational evidence to decide what deserves the next investment.
If you are planning a SaaS product, map one real customer journey from signup to recurring value, list every state that can affect access, and identify the evidence that would justify expanding the product. That gives the team a more reliable starting point than a feature list or a technology-first estimate.
Also published on

Share post on




Related Articles


How Will AI Affect Software Development? Complete Guide In 2026
How Will AI Affect Software Development? Complete Guide In 2026 Published October 21, 2026
Mobile App Development Process: Seven Stages From Idea To Launch
Mobile App Development Process: Seven Stages From Idea To Launch Published October 20, 2026
TOP 5 iOS App Development Languages: Swift, Objective-C & Cross-Platform
TOP 5 iOS App Development Languages: Swift, Objective-C & Cross-Platform Published October 16, 2026